Features Pricing Open source Docs
Theme
Language
fr en de es pt sv nl cs ko ja zh
Sign in
CONTINUOUS SECURITY · SELF-HOSTED OR CLOUD

Keep your environments secure, around the clock.

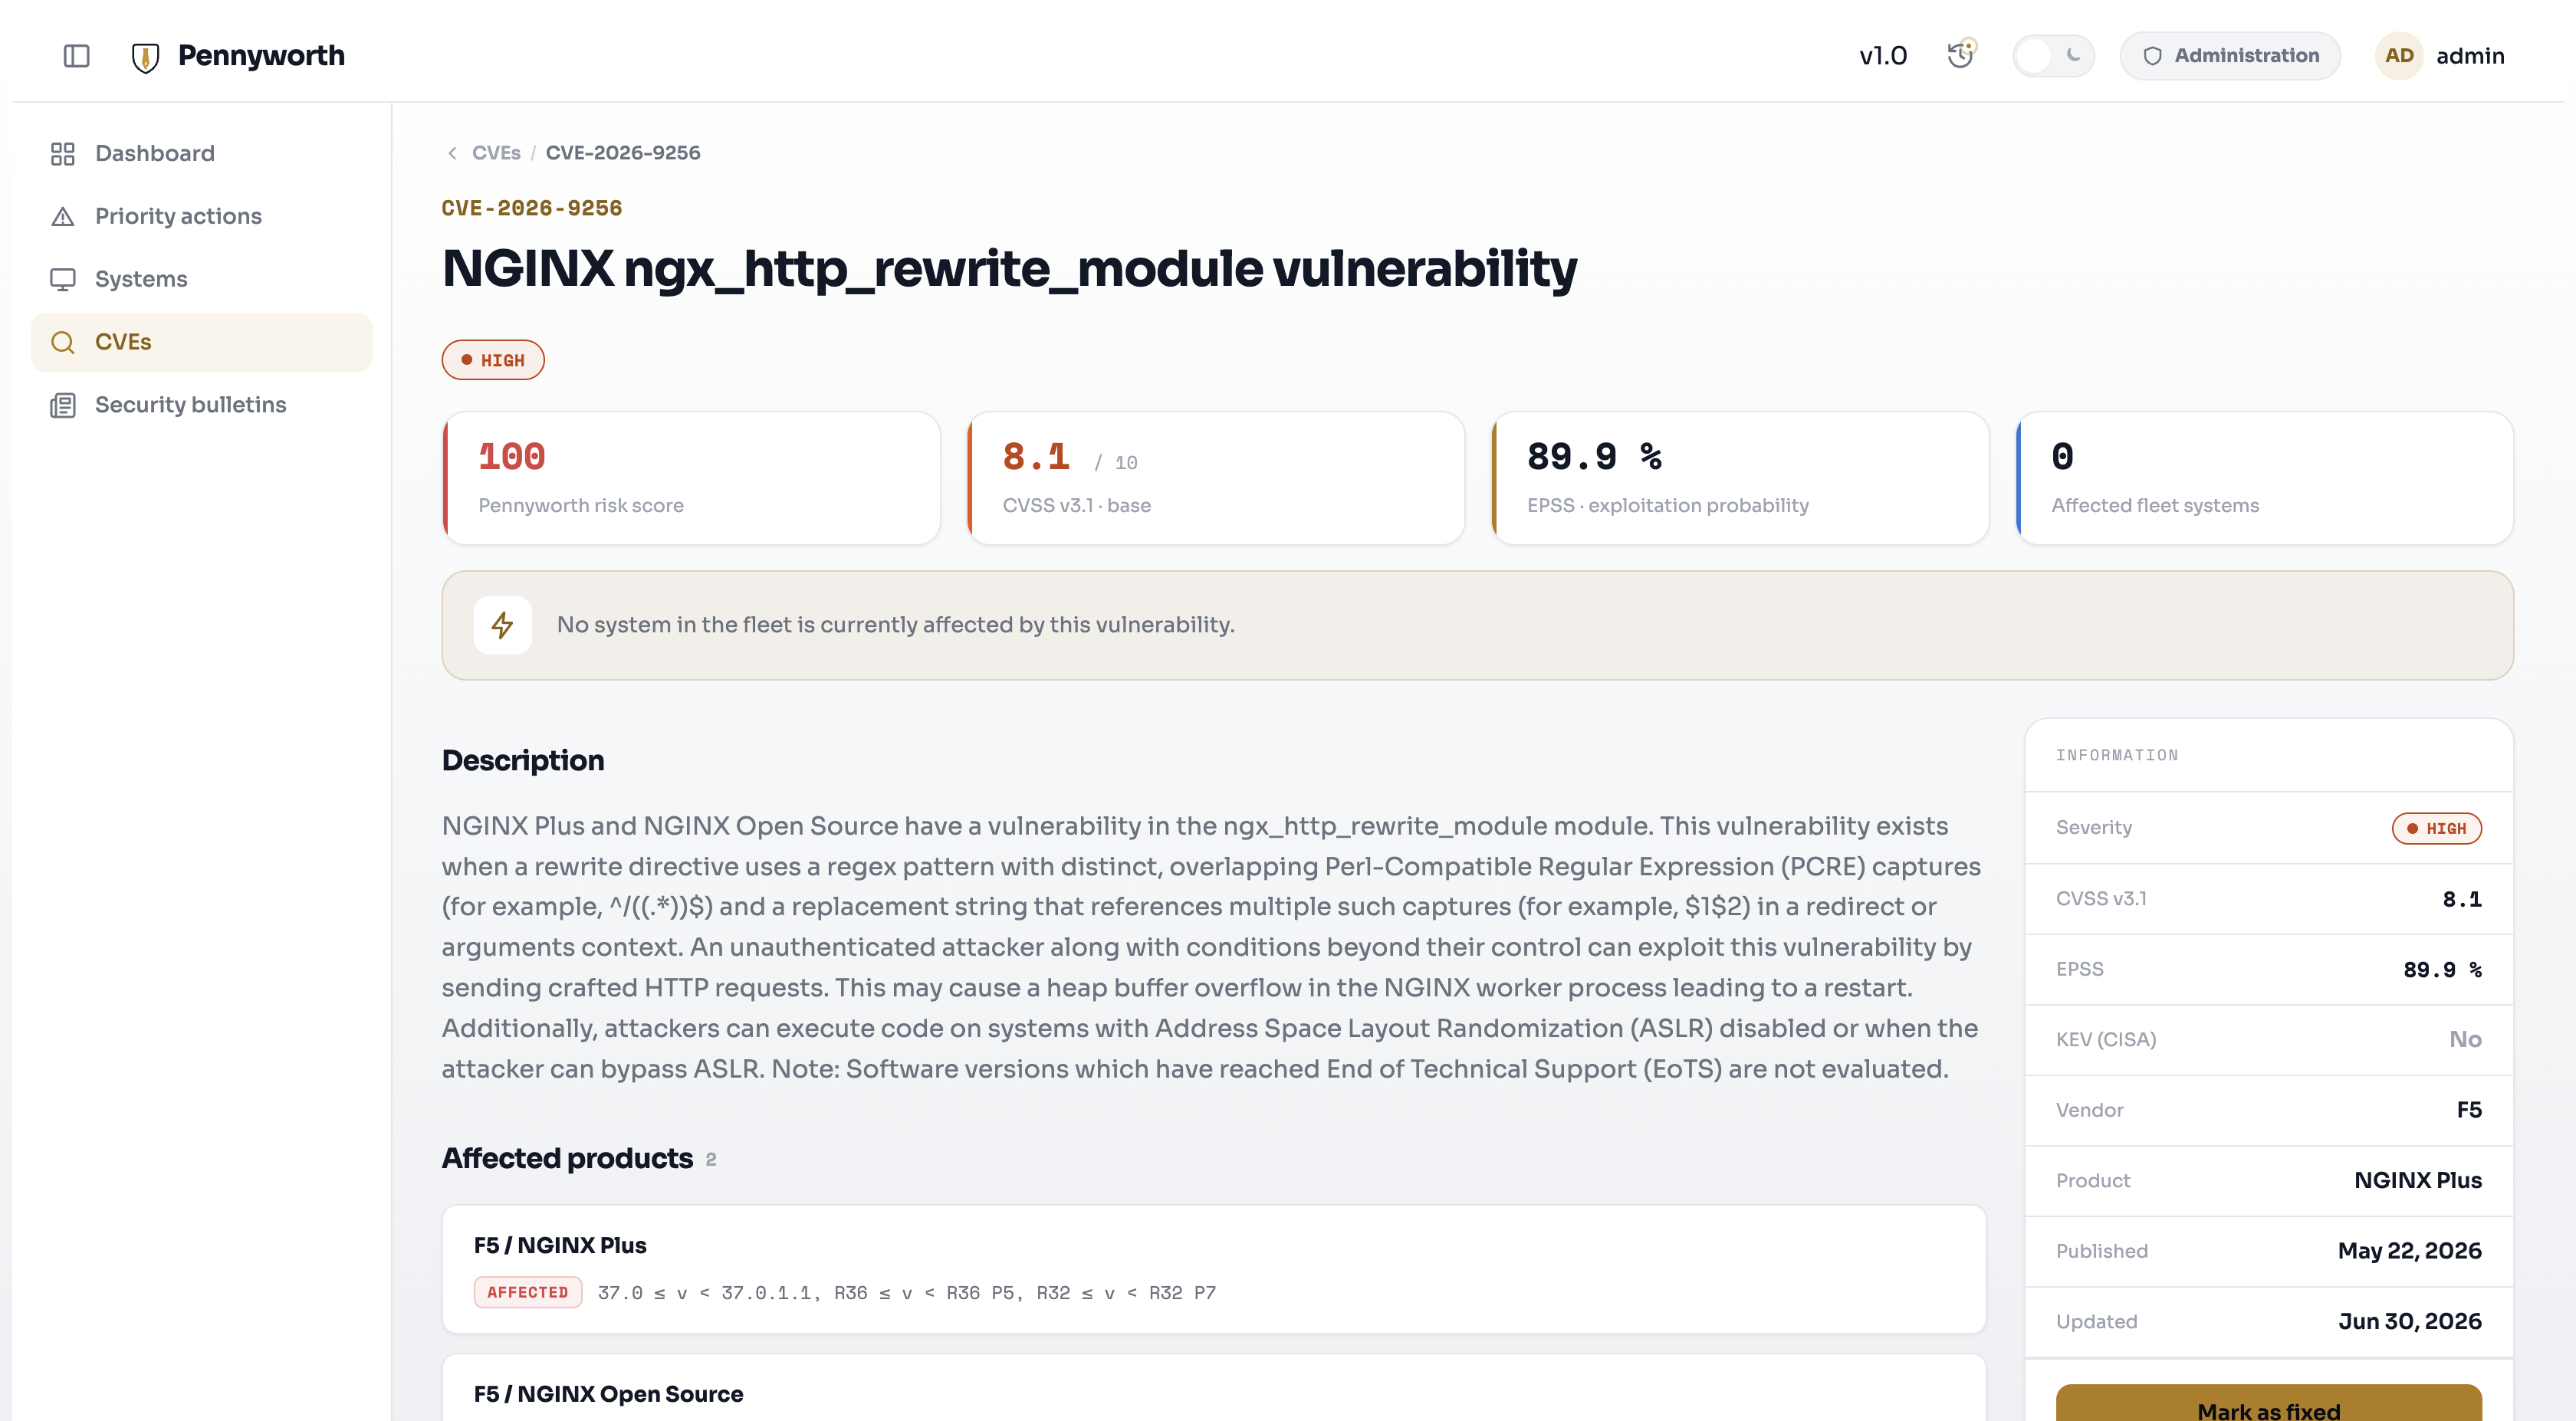
Pennyworth continuously monitors your fleet and cross-references each detected vulnerability with real exposure signals (EPSS, the CISA KEV catalog, actual presence on your systems) to help you prioritize remediation.

$ curl -fsSL get.pennyworth.cc | sh
Pennyworth dashboard preview
MITRE, EPSS, CISA KEV
Correlated sources
SSH · agents
On-premise collection
LDAP · OIDC · SAML
External auth compatible
Apache-2.0
Community license
Features

Built to sort signal from noise, not to stack up CVEs.

◎
Real risk score
Severity, EPSS and presence in the CISA KEV catalog combined — not a raw CVSS sort.
▤
Continuous inventory
SSH satellites per site or agents per machine. Packages, versions, EOL tracked continuously.
⌗
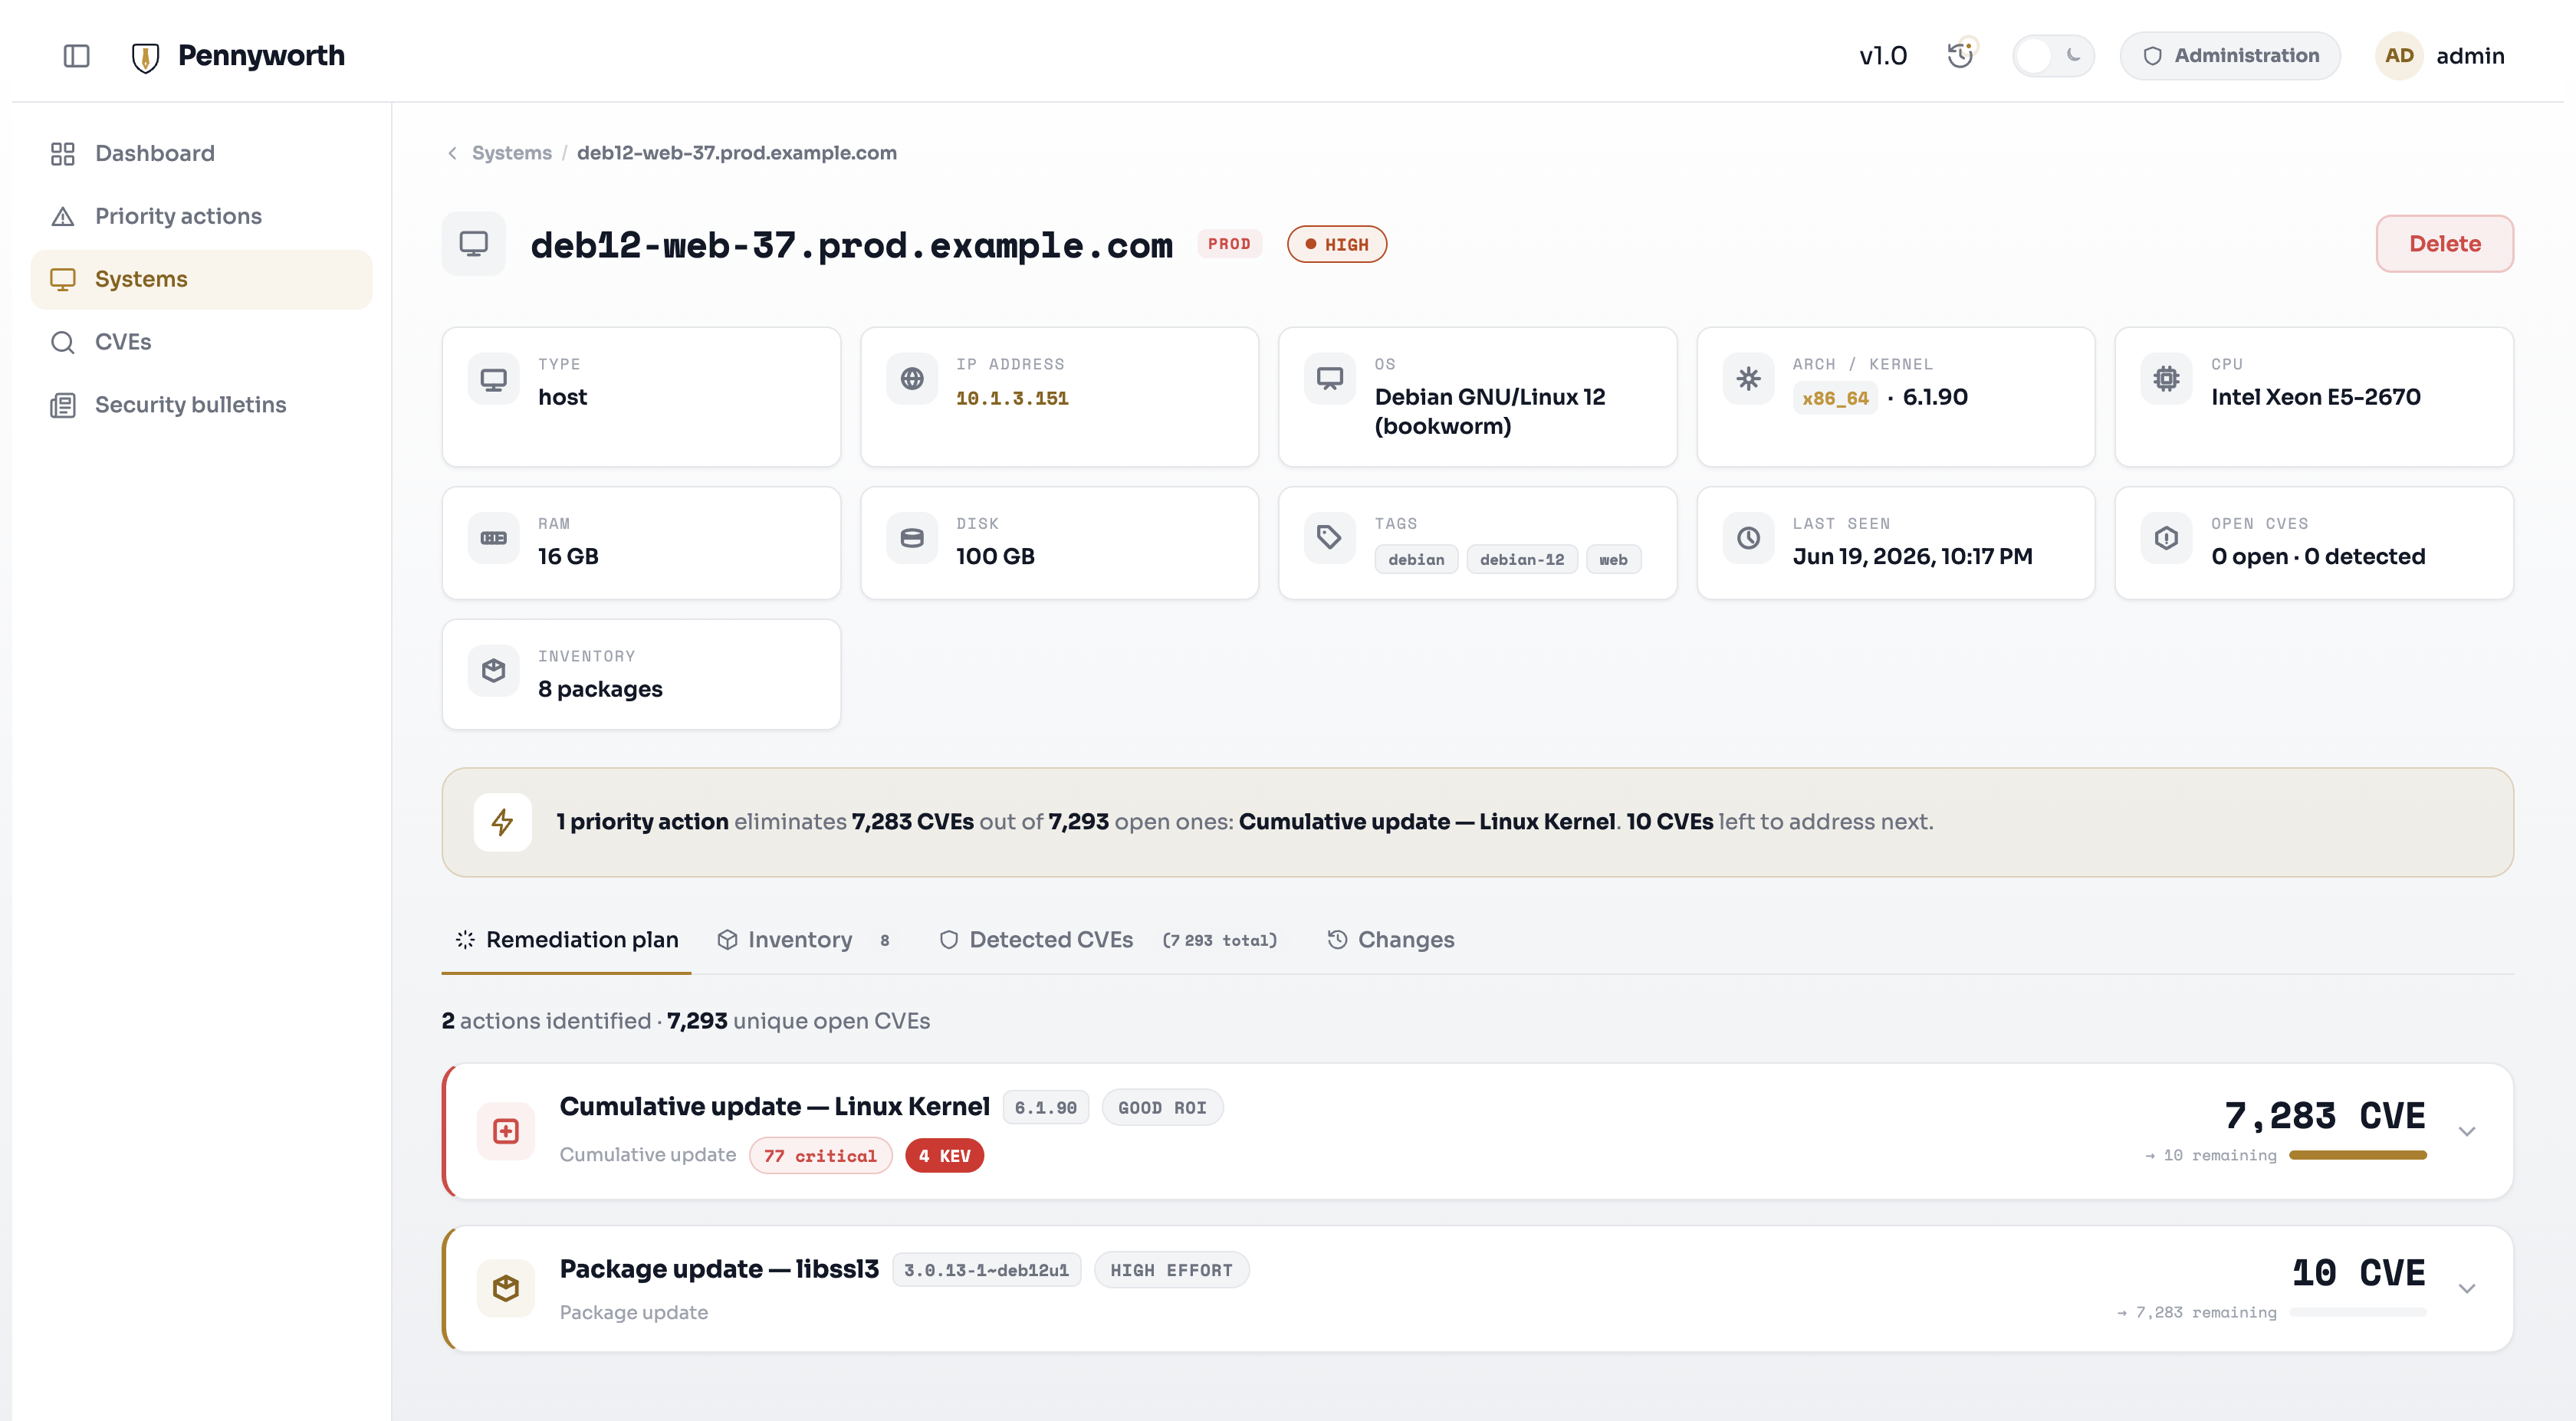
Remediation plans
Each action (patch, migration) ranked by the real number of CVEs it eliminates, not raw volume.
⌁
Automated sync
MITRE, EPSS, CISA KEV and bulletins (CERT-FR…) refreshed then recomputed in a pipeline.
Pennyworth action plan preview
Open source

Open code, auditable, self-hostable.

The Community Edition runs on your own infrastructure — no inventory data ever leaves it. Cloud runs the exact same engine, hosted and maintained by us.

# github.com/pennyworth-security
$ git clone https://github.com/pennyworth-security/pennyworth-core.git
$ docker compose up -d
→ console available at :8443
Pricing

Community, self-hosted. Cloud, fully managed.

Community
Self-hosted, open source
Free
  • Risk-based prioritization
  • Unlimited inventory & collectors
  • CVE, EPSS, CISA KEV
  • GitHub community
View on GitHub
Demo instance
No sign-up
0 €
  • Preloaded sample fleet
  • Reset every 24 hours
  • Instant access, nothing to install
Launch demo →

Frequently asked questions

Is the Community Edition limited?

No — inventory, collectors and vulnerability sources are unlimited. Cloud adds hosting, high availability and SSO.

How does the demo instance work?

A shared account, preloaded with a sample fleet, no sign-up required. It's reset every 24 hours.

Which vulnerability sources are covered?

MITRE CVE, EPSS, the CISA KEV catalog, and bulletins (CERT-FR, BSI…) — synced then recomputed in a pipeline.

How do systems report their inventory?

Via satellites (SSH collection per site) or agents installed directly on the machine.

Stay ahead of the threats that matter.

Create a cloud account Try the demo →